The perimeter has moved
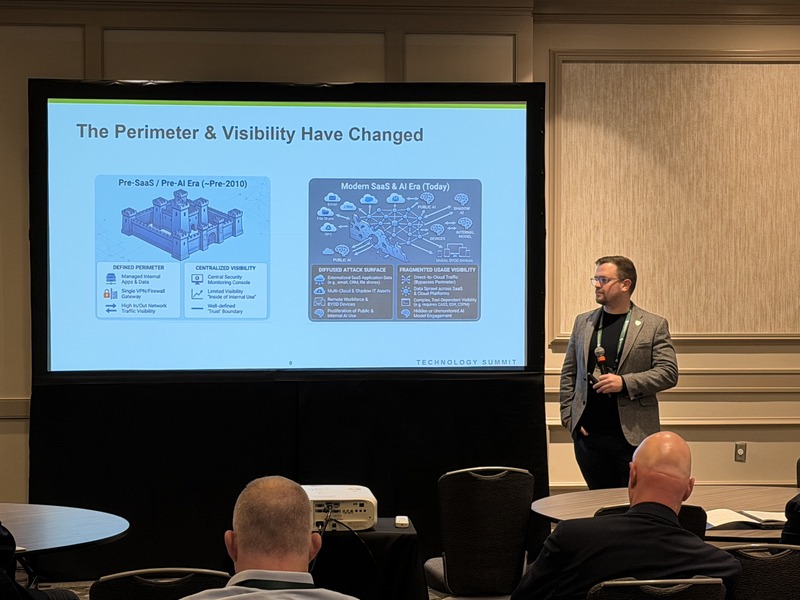
Jake Nix opened with a simple idea: the old network perimeter no longer describes where your risk actually sits. Data now lives across dozens of SaaS platforms, identity has become the main control point, and AI tools are creating new ways for information to leave the business.
He walked through how teams can rebuild visibility without trying to recreate the old castle-and-moat model, starting with an accurate inventory of systems, vendors and data flows.
Compliance as a business advantage
In the second session, Tony Bai looked at how SOC 2, ISO 27001 and supply chain reporting are shifting from checkbox exercises to something buyers actively ask for during procurement. Organizations that can show clear, current evidence of their controls are closing deals faster and spending less time on security questionnaires.
What we heard from attendees
Both sessions were full, and the questions afterwards were practical. Most people wanted to know where to start, how to prioritize when resources are tight, and how to stop compliance work becoming a once-a-year scramble.
Third-party and SaaS risk, continuous evidence collection and guardrails for AI use came up again and again. So did the challenge of mapping one set of controls to several frameworks at once.
Thanks for stopping by
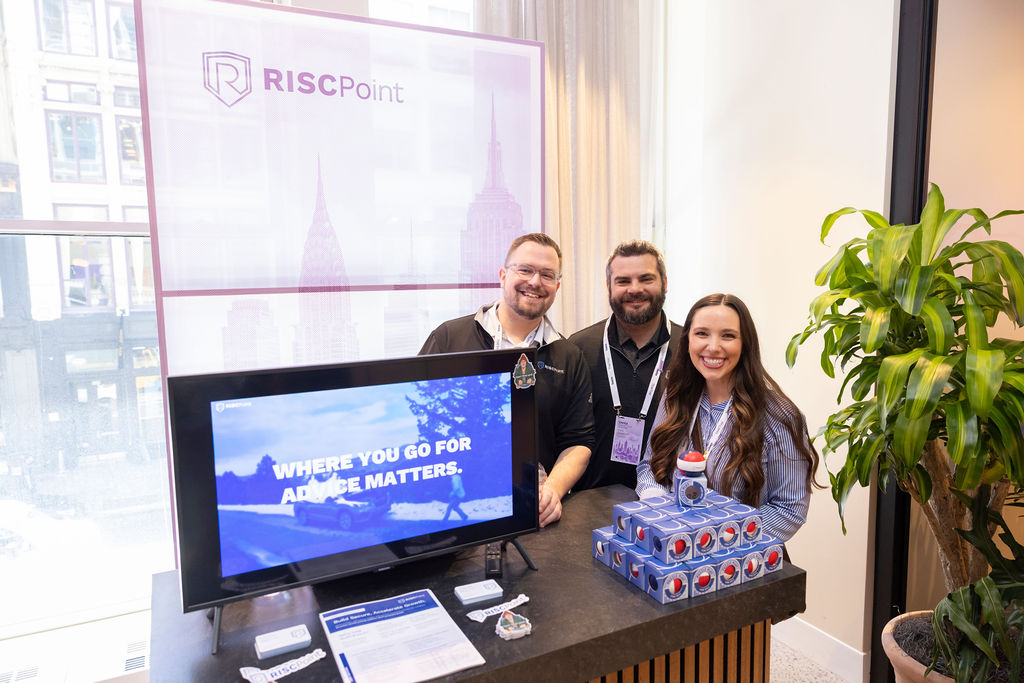
Thank you to everyone who attended our sessions or came over to say hello. If you'd like to continue the conversation or get a copy of the slides, get in touch with our team and we'll follow up.
Stay Informed, Stay Secure
Subscribe to our newsletter and get the latest cybersecurity insights, updates, and event invitations delivered straight to your inbox. Join our community and empower your security journey with RISCPoint's expert knowledge.
Join our newsletter for updates. Terms.